Capture Intel.
Connect the Threat.
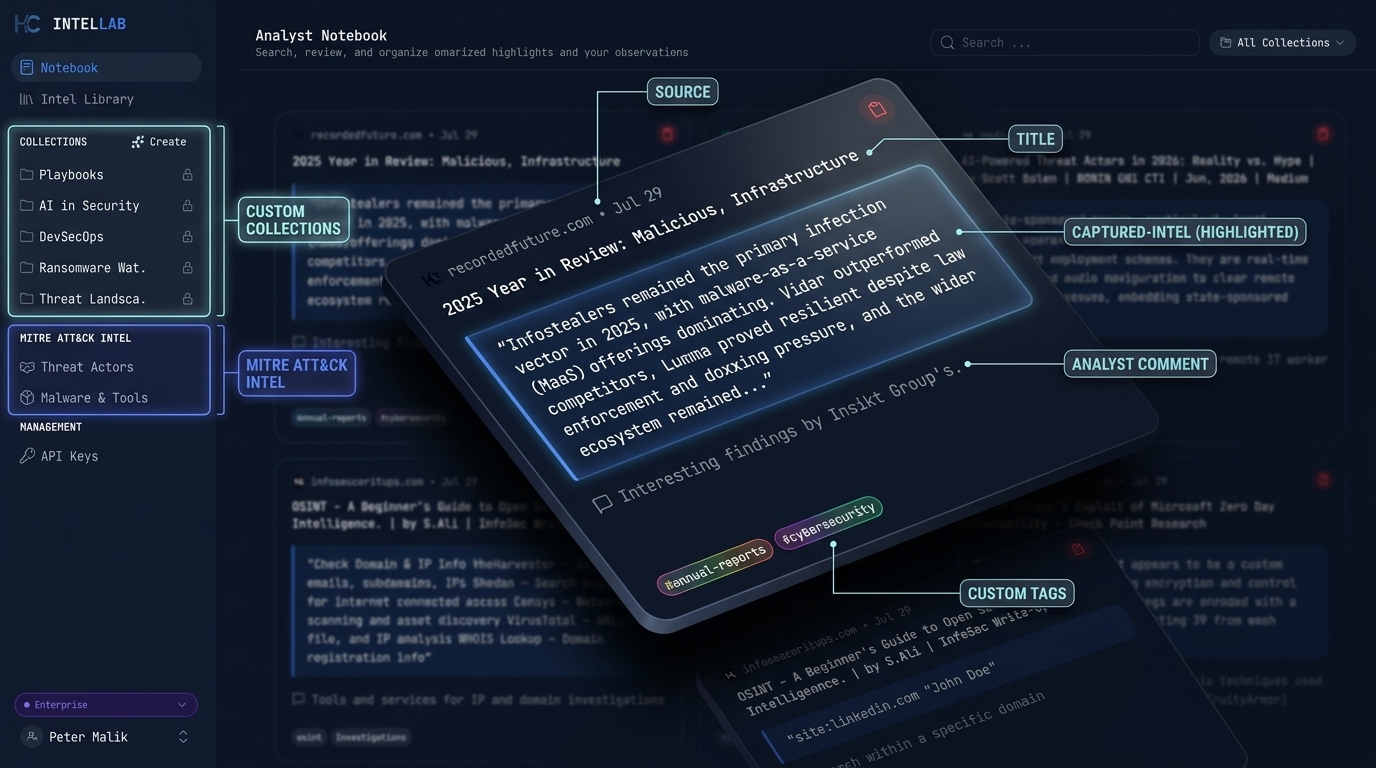
Turn daily reading into structured intelligence. Capture intel from web pages, reports, and articles, link threat actors & malware to entities, and map behaviors to MITRE ATT&CK in a unified analyst workspace.
- Capture highlights & evidence
- Custom entities & asset mapping
- MITRE ATT&CK mapped
- Collaborative workspaces & comments
What You Can Do
Capture Intel
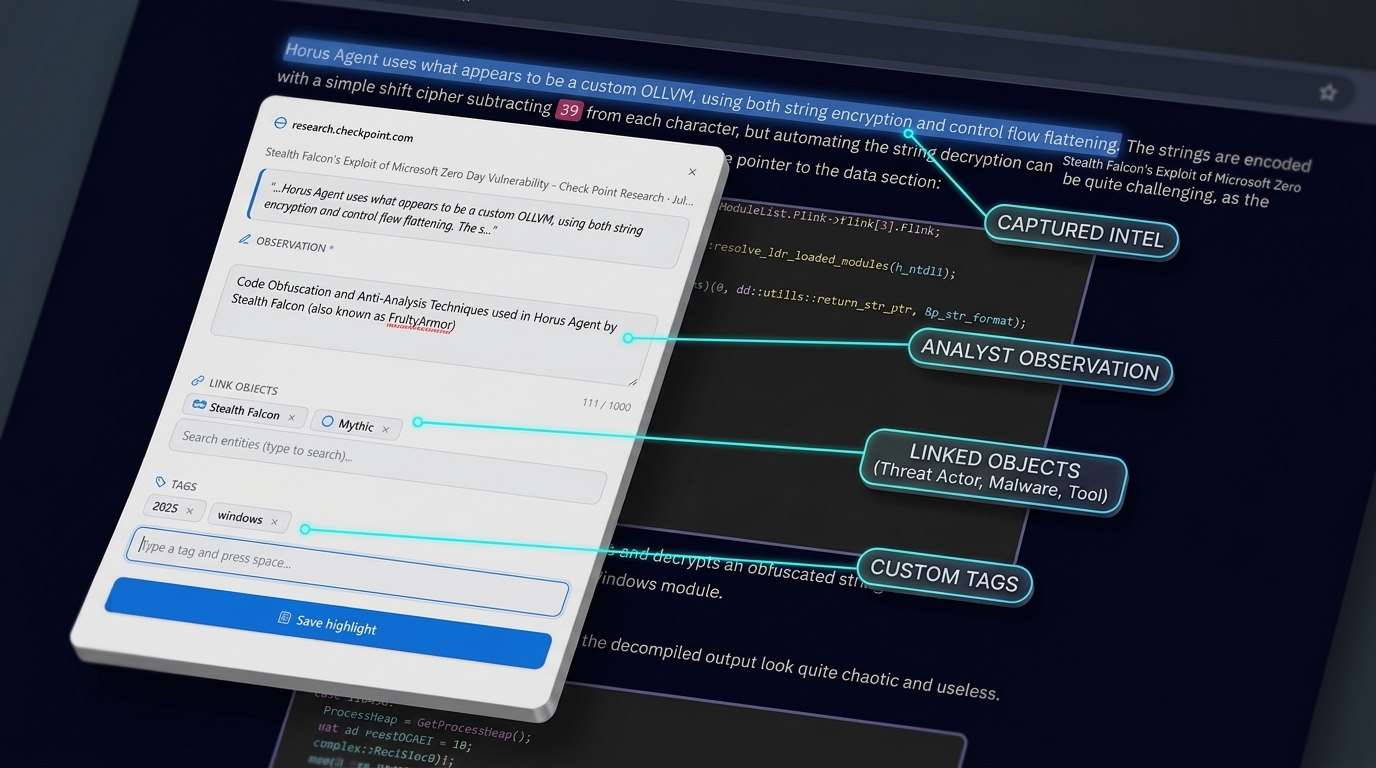
Highlight and record intel directly from any webpage using a lightweight browser extension without interrupting your research workflow.
- Captures URL, page title, timestamp, and text highlights automatically
- Attach contextual notes & tags directly to captured evidence
- Link findings to threat actors, malware, tools, and custom entities
Subscription Tiers
Choose the right plan for individual threat research or team-wide threat actor and entity tracking.
Free
No Credit Card RequiredFor community cybersecurity researchers and hobbyists starting out.
- 200 Captured Highlights
- 50 Created Entities
- Up to 5 Collections
PRO
For independent professional threat analysts and cybersecurity researchers.
- Unlimited Captured Highlights
- Unlimited Created Entities
- Unlimited Collections
Enterprise
For threat intelligence teams and analysts collaborating across organizations.
- Unlimited Highlights, Entities & Collections
- Up to 15 Shared Seats
- Shared Team Workspaces
On-Prem
Air-gapped deployment for high-compliance and strict data sovereignty environments.
- Isolated Air-Gapped Deployment
- Dedicated Offline Data Updates
- Custom Threat Data Integrations
Ready to centralize your
cyber intelligence?
Start capturing and connecting intel today. Our team ships new capabilities every week — see what's live and what's next on the roadmap.
See what's coming next
Check our public roadmap or request a feature.
★ Magic Link Access
Frequently Asked Questions
Everything you need to know about capturing evidence, building threat graphs, and collaborating.